DOCKFINITY
Build & Market Discovery

Python packaging and runtimes harden supply chains

Python packaging and runtimes harden supply chains

  • TOOLING
Release0.13.522 October 2026

uv

An extremely fast Python package and project manager written in Rust that updates managed CPython builds and certificate stores.

Bundles python-build-standalone 20261021 with Python security patches and removes compromised eMudhra root certificates via rustls-webpki.

Licence
Apache-2.0
Platform
Apple Silicon macOS, Intel macOS, ARM64 Windows, x86 Windows, Linux
Releasev2.9.821 October 2026

deno

A modern runtime for JavaScript and TypeScript with built-in bundling, testing, and strict security defaults.

Distrusts compromised eMudhra certificate authorities and fixes dynamic import permission checks for compiled binaries.

Licence
MIT
Platform
Apple Silicon macOS, ARM64 Windows, ARM64 Linux, x86_64 Linux

What this changes

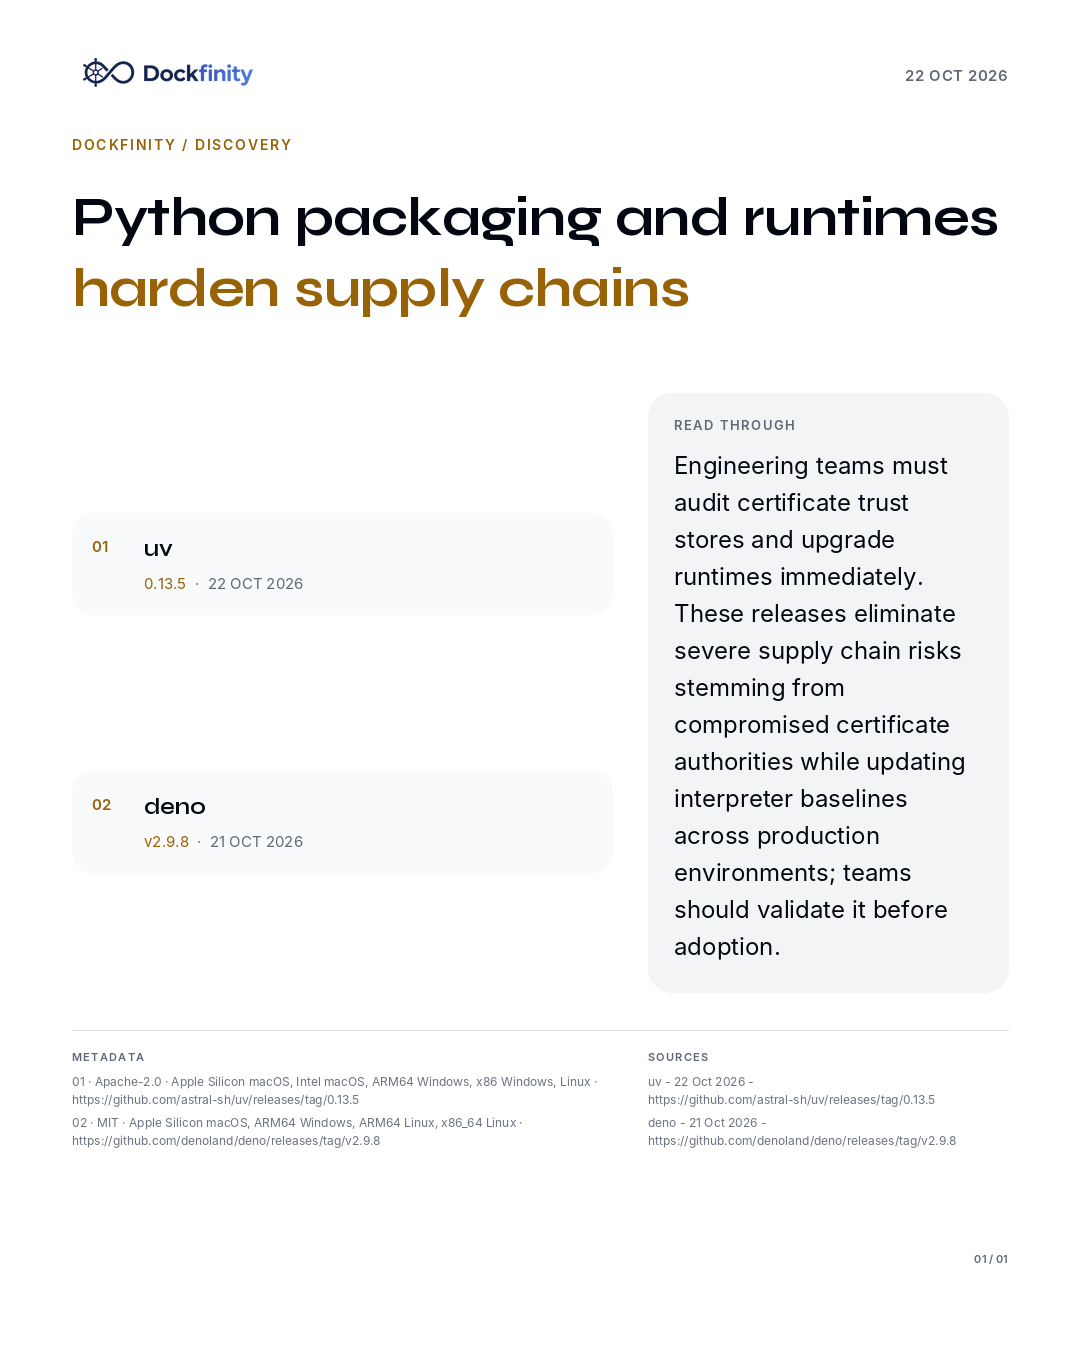
Engineering teams must audit certificate trust stores and upgrade runtimes immediately. These releases eliminate severe supply chain risks stemming from compromised certificate authorities while updating interpreter baselines across production environments; teams should validate it before adoption.

The card

Python packaging and runtimes harden supply chains — the card published on 22 October 2026

The same card posted on social. Open it for the full size.

Sources

Source: astral-sh/uv, 22 Oct 2026 - https://github.com/astral-sh/uv/releases/tag/0.13.5; Source: denoland/deno, 21 Oct 2026 - https://github.com/denoland/deno/releases/tag/v2.9.8

Independent technology analysis published by Dockfinity. Every release, version, licence and figure carries the primary source it was read from.

All briefs